

Joe Security Launches 'Joe Sandbox A1' for Precise Malware Analysis
 Published2018.01.26 11:02
Execution and analysis of malware on actual NUC hardware
Insec Security announced that Joe Security is launching 'Joe Sandbox A1,' the world's first appliance for precise malware analysis on bare metal (non-virtualized physical servers).
The Joe Sandbox A1 is a standalone device based on an ultra-compact NUC (Next Unit of Computing) PC form factor, equipped with Joe Sandbox Desktop (equipped with malware analysis capabilities for desktop and mobile devices).
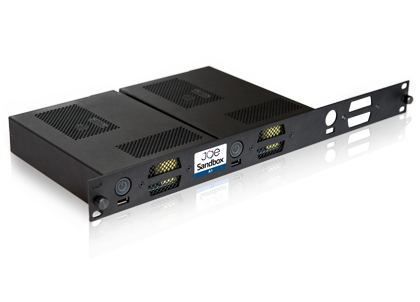
Recently, malware easily detects and bypasses virtual machines used by sandboxes. A1 does not use virtual machines such as VirtualBox, VMware, or KVM, but analyzes malware directly on actual physical NUC hardware. In particular, it supports malware analysis on all networked operating systems using Hypervisor Based Inspection (HBI) technology.
In addition to the above, it provides analysis based on over 959 malicious behavior signatures to detect and classify various malicious activities. Notable features include the Yara method, dynamic VBA and JavaScript analysis, and HCA support.
Comments
Related news
Opswat Launches Malware Detection Solution That Rapidly Detects Threats Using CDR Technology
Insecurity announced that Opswat, a specialist in malware detection, has released the latest version of MetaDefender, a malware detection solution that upgrades file scanning and anti-malware cloud services. The newly unveiled version 4.8 of MetaDefender Cloud enables developers and malware analysis experts to scan files faster and detect threats by leveraging CDR technology for multiscanning and data sanitization. Opswat particularly supports synchronization between the latest maintenance release for on-premises products and cloud services through this new product, and has improved end-user performance through expanded file scan capacity. Additionally, by supporting over 30 file types and over 110 file transformations, it provides industry-leading data sanitization coverage.
2018.01.04by 김지혜 기자
Argus Cyber Security and ST Partner for Connected Vehicle Technology Security
Argus Cyber Security and STMicroelectronics (ST) have announced a collaboration to enhance cyber security for connected vehicle technology. Telematics and infotainment devices are becoming increasingly complex to support advanced connected services, making them more vulnerable to cyber attacks. Protecting these devices from cyber threats requires more sophisticated multi-layered security, and continuous monitoring must be implemented throughout the vehicle's lifecycle. Through joint efforts, the two companies are integrating Argus Connectivity Protection into ST's automotive microprocessor Telemaco3P, enabling real-time detection and prevention of attacks on automotive telematics devices and preventing attacks from spreading across in-vehicle networks.
2018.01.11by 김지혜 기자
Databricks Unveils Open AI Security Monitoring 'Lakewatch'
Databricks entered the security market on March 24 by unveiling LakeWatch, an open-source agentic SIEM. The core functionality of this product is to integrate and analyze security, IT, and business data in a single environment to support AI-based threat detection and investigation. The company explained that it reduces the limitations of existing security operations centers, which have had to forgo some data due to high cost structures, and enables large-scale data analysis and automation based on open formats and ecosystems. LakeWatch is currently offered as a private preview, with Adobe and Dropbox mentioned as early customers. Databricks also announced an expanded partnership with Anthropic as well as the acquisition of Antimatter and SiftD.ai.
2026.03.26by 배종인 기자
Kaspersky Unveils Revamped 'NEXT' Combining SOC Integrated Management and AI Analytics
As enterprises increase demand for integrated management and automation in the construction and operation of Security Operations Centers (SOC), Kaspersky has disclosed updates to its B2B security product suite 'Kaspersky Next'. This update expands EPP, EDR, XDR, and SIEM integration through a single console based on OSMP, incorporates AI capabilities such as DLL hijacking detection and suspicious account takeover behavior identification, and includes integration with generative AI assistant tool KIRA. The company stated that in large-scale deployment environments, EDR Expert can reduce resource requirements by up to 30%, and XDR Expert by up to 60%.
2026.03.25by 배종인 기자
Samsung Electronics Smart Monitor Acquires First International Certification… Expanding Application Scope Following TVs
Samsung Electronics has received Common Criteria (CC) certification for 'Samsung Knox,' a security solution applied to its 2026 smart TVs and smart monitors. The smart TV has achieved certification for 12 consecutive years, while the smart monitor obtained industry-first certification this time. The evaluation was conducted focusing on core functions including kernel integrity monitoring, phishing site blocking, and unauthorized execution prevention. The company plans to expand the scope of security certification beyond TVs to monitors, responding to growing personal information protection requirements as connected devices proliferate.
2026.03.25by 배종인 기자