

Insec Security Launches Maestro Mobile Forensics, a Mobile Malware Detection Solution
 Published2018.03.12 11:06
Utilizing the machine learning-based Maestro Cybersecurity Threat Intelligence Integrated Platform
Maestro Networks, an in-house venture in which Insec Security has invested, jointly conducted technology research, and is in charge of research and development, announced the launch of ‘Maestro Mobile Forensics,’ a mobile forensics solution that extracts mobile apps and detects and analyzes malicious apps at high speed.
'Maestro Mobile Forensics' is a Korean-style forensic product that is a mobile forensic tool that detects and analyzes mobile malware. It can extract apps from mobile phones and quickly detect and precisely analyze large amounts of malware.
This extracts all installed mobile apps from the device and transmits them to the Maestro Cyber Threat Intelligence Platform (CTIP), which automatically analyzes, verifies, and blocks files for malware. Various verification solutions linked to Maestro CTIP are then utilized to quickly and accurately detect and analyze malicious apps.
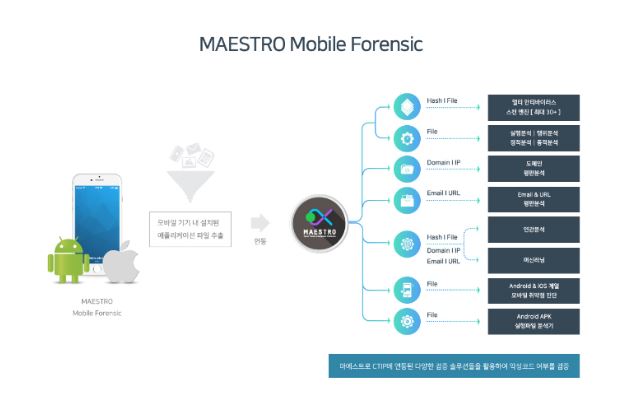
Maestro CTIP is an intelligent security intelligence integrated platform that can detect, analyze, and block malware using file, IP/Domain/URL, email analysis, correlation analysis, and machine learning analysis flowing into the enterprise. Maestro CTIP integrates with various endpoint, network, email, and web security solutions deployed in-house to quickly identify and respond to threats such as the latest ransomware, advanced persistent threat (APT) attacks, and malware. Maestro supports integration with network and endpoint security solutions from Symantec, Cisco, AhnLab, F5 Networks, Carbon Black, FireEye, and Palo Alto Networks during the file ingestion phase, and with Opswat Metadefender, ZoSecurity, and DomainTools during the file verification phase.
“Maestro Mobile Forensics works in conjunction with Maestro CTIP to help quickly detect and analyze ransomware, advanced persistent threat (APT) attack codes, and other malware,” said Jong-kwang Kim, CEO of Insec Security.
Comments
Related news
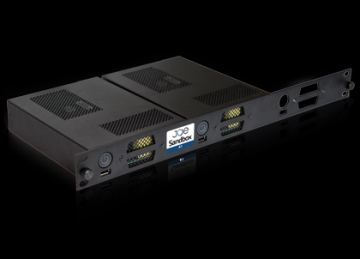
Joe Security Launches 'Joe Sandbox A1' for Precise Malware Analysis
Insecurity announced that Joe Security has launched "Joe Sandbox A1," the world's first malware precision analysis appliance for bare metal (non-virtualized physical servers). Joe Sandbox A1 is a standalone device based on a ultra-compact NUC (Next Unit of Computing) PC form factor with Joe Sandbox Desktop (equipped with malware analysis capabilities for desktop and mobile devices) installed.
2018.01.26by 김학준 기자
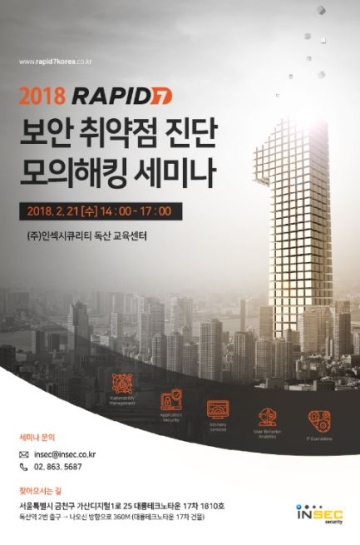
Insecurity holds '2018 Rapid7 Security Vulnerability Diagnosis Penetration Testing Seminar'
Insecurity announced that it will hold the '2018 Rapid7 Security Vulnerability Diagnosis Penetration Testing Seminar' for corporate security managers, introducing security vulnerability diagnosis and testing, penetration testing, and response measures. At this seminar, Insecurity will present security vulnerability diagnosis and methodology for enterprise infrastructure as a whole, response methods through penetration testing and intrusion simulation, and web application vulnerability management strategies. The Rapid7 product suite provides asset status and security and compliance vulnerability information for the entire IT infrastructure within an organization through a centralized dashboard. Additionally, experts can automate simulations to defend against hacking attacks with the Rapid7 product suite, automatically diagnosing diverse security vulnerabilities worldwide and enhancing the security stability of corporate assets through penetration testing.
2018.02.13by 김학준 기자
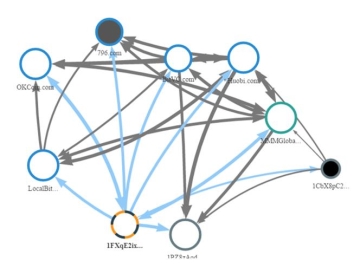
Insec Security Launches Digital Forensic Solution for Blockchain and Bitcoin Account Analysis
Insecurity announced that Chainalysis, a software specialist in bitcoin anti-money laundering, has launched Chainalysis REACTOR, a digital forensics solution for blockchain and bitcoin account analysis. Chainalysis REACTOR is a transaction analysis solution based on bitcoin wallet addresses that allows users to easily analyze all transaction logs of a wallet by entering the wallet address. As an interactive investigation tool, REACTOR enables annotations and notes to be added to investigation results, allowing simultaneous investigations through data sharing with other members of the same organization.
2018.02.21by 김지혜 기자
Databricks Unveils Open AI Security Monitoring 'Lakewatch'
Databricks entered the security market on March 24 by unveiling LakeWatch, an open-source agentic SIEM. The core functionality of this product is to integrate and analyze security, IT, and business data in a single environment to support AI-based threat detection and investigation. The company explained that it reduces the limitations of existing security operations centers, which have had to forgo some data due to high cost structures, and enables large-scale data analysis and automation based on open formats and ecosystems. LakeWatch is currently offered as a private preview, with Adobe and Dropbox mentioned as early customers. Databricks also announced an expanded partnership with Anthropic as well as the acquisition of Antimatter and SiftD.ai.
2026.03.26by 배종인 기자
Kaspersky Unveils Revamped 'NEXT' Combining SOC Integrated Management and AI Analytics
As enterprises increase demand for integrated management and automation in the construction and operation of Security Operations Centers (SOC), Kaspersky has disclosed updates to its B2B security product suite 'Kaspersky Next'. This update expands EPP, EDR, XDR, and SIEM integration through a single console based on OSMP, incorporates AI capabilities such as DLL hijacking detection and suspicious account takeover behavior identification, and includes integration with generative AI assistant tool KIRA. The company stated that in large-scale deployment environments, EDR Expert can reduce resource requirements by up to 30%, and XDR Expert by up to 60%.
2026.03.25by 배종인 기자