

Gartner "41% of CISOs Experience Deepfake Voice Call Attacks"
 Published2026.09.28 15:49
According to the survey, 41% of respondents reported experiencing at least one social engineering attack using deepfakes in employee voice calls over the past 12 months.
The percentage of respondents who experienced the same type of attack in video calls was 36%.
The rate of experiencing email phishing, spear phishing, and business email compromise incidents was 79%, while vishing and smishing accounted for 58%.
The explanation is that establishing verification and reporting as basic behavior in response to high-risk requests is more effective than training on 'how to identify fakes'.
Phishing-resistant authentication and risk-based identity controls should be applied to critical business processes such as account recovery, privileged access, and payment authorization, and mechanisms are needed to detect unauthorized use of identity information even after normal login.
Impersonation reports should be analyzed in correlation with account recovery history, new device access, permission changes, and financial transaction data, and incident response manuals should be updated to include compromised or misused AI agents.
Comments
Related news
Gartner, "10% of Companies to Transition to AI First by 2030"
Gartner announced six major data and analytics (D&A) trends that enterprises should reflect in their strategies over the next two years on June 17, forecasting that more than 10% of global enterprises will transition to "AI-first" companies by 2030, where AI serves as a core benchmark for all decision-making and investments, thereby securing competitive advantage. The firm identified AI agents, semantics, and integrated D&A platforms as key drivers, and presented sovereign AI acceleration and governance, agentic data streaming for real-time response, and GraphRAG, which combines knowledge graphs and LLMs, as major trends.
2026.06.17by 명세환 기자

Gartner: “NeoCloud to Capture 20% of AI Cloud Market by 2030”
Gartner forecasted on the 24th that as GPU-intensive computing demand surges due to generative AI proliferation, neocloud providers specializing in AI and high-performance workloads will capture 20% of the $267 billion AI cloud market by 2030. With legacy hyperscalers unable to keep pace with GPU demand and data sovereignty requirements serving as growth drivers, Gartner recommended that IT leaders evaluate sovereign neoclouds and diversify their cloud strategies to address GDPR and EU AI Act compliance.
2026.06.24by 명세환 기자
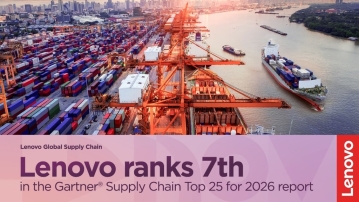
Lenovo Ranks 7th Globally in Gartner's Supply Chain Leadership 25
Lenovo ranked 7th globally in Gartner's supply chain leader rankings. By implementing the AI-based supply chain orchestration system 'iChain', the company improved decision-making speed by 60% and reduced analysis time from the conventional 2-3 weeks to 2-3 hours. Currently operating over 30 manufacturing sites and thousands of partners worldwide, Lenovo is expanding its global manufacturing network in Saudi Arabia, the United States, Mexico, and other regions.
2026.06.25by 배종인 기자

Gartner: “Agentic AI Reshapes SaaS Market… ‘SaaS Pocalypse’ Begins in Earnest”
Gartner forecasts that the proliferation of agentic AI will fundamentally reshape enterprise application spending up to 362 trillion won by 2030. As agentic systems bypass traditional SaaS interfaces, the connection between user count and revenue growth is expected to weaken, and enterprise purchasing criteria are predicted to shift from feature-based to outcome-focused evaluation. Existing software vendors will need to transition to outcome-based value propositions and integrate agentic capabilities in order to survive.
2026.07.02by 명세환 기자
Gartner: “60% of Companies Expected to Adopt Micro-teams in AI Era by 2029”
Gartner forecasts that software engineering organizations in the AI era will transform into micro-teams of 4-5 people. Adoption among enterprises is expected to increase fourfold, rising from 15% in 2026 to 60% in 2029, representing a reorganization aimed at optimal combining of human and AI capabilities. However, caution is warranted as the reduction in hiring new employees could result in gaps in knowledge transfer and talent pipeline development.
2026.07.08by 명세환 기자